Stuxnet: the Most Menacing Malware in History
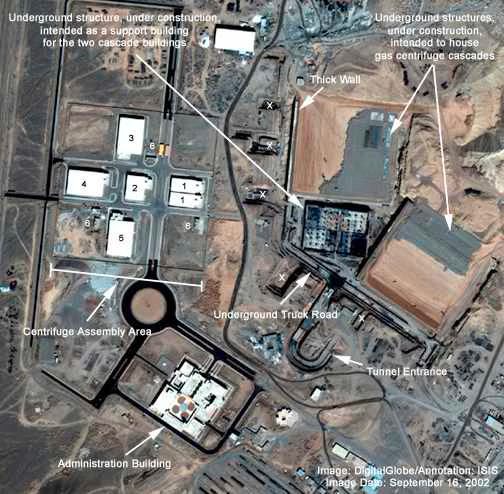
If you have some time on your hands, you should head over to Wired for fascinating read on Stuxnet, a piece of malware discovered in Belarus on June 17, 2010.
Researchers discovered that the malware targeted a specific nuclear plant in Iran. Was Israel or the U.S. behind it? No one knows. But this was the first of it's kind to be discovered.
It reads like a spy novel. Great job from Wired.
Some tidbits:
It was a messy and imprecise method of attack — a little like infecting one of Osama bin Laden’s wives with a rare virus, hoping she’d pass it to the Al Qaeda leader. It was bound to infect others beyond the target, increasing the chance that the plot would be discovered.This is exactly what happened with Stuxnet.
In the end, Stuxnet’s creators invested years and perhaps hundreds of thousands of dollars in an attack that was derailed by a single rebooting PC, a trio of naive researchers who knew nothing about centrifuges, and a brash-talking German who didn’t even have an internet connection at home.